
Updates

Follow new updates and improvements to Spacelift.

Introducing Git Checkout Options in Spacelift

We’re excited to announce the general availability of the “Use Git checkout” option in VCS integration settings. This update gives customers more flexibility and control over how repositories are checked out, including support for sparse checkout in stack settings.

Git sparse checkout allows you to check out only a subset of files from a repository, rather than the entire working directory. This is particularly useful for large repositories where you only need to work with specific directories or files.

Previously, we attempted to enable Git Checkout globally across all environments. However, differences in customer needs made a universal rollout impractical. With this release, teams can now opt in at their own pace, making migration smoother and safer.

With this release, you can:

  • Opt-in to Git Checkout, and enable or disable:

    • Individual (One VCS check for each Stack) and / or;

    • Aggregate (Summarize checks across all affected Stacks into a predefined set)

  • Configure Git Sparse Checkout Paths

Be sure to check out these new features, and let us know what else you would like to see added next.
New

Introducing Advanced Access Control in Spacelift

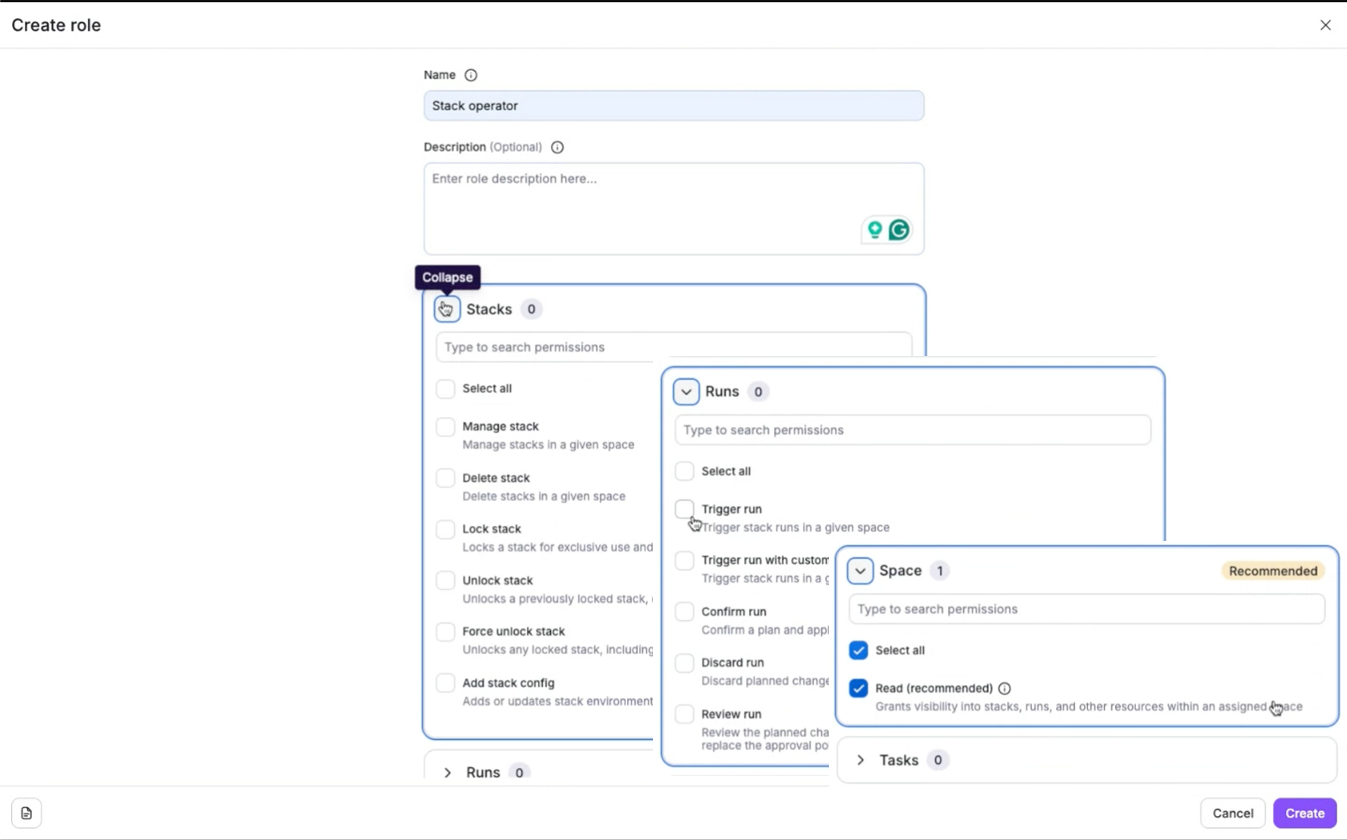
We’ve reimagined Spacelift’s authorization model with Advanced Access Control (AAC) — fine-grained, role-based permissions that go beyond the old read/write/admin boundaries.

Now, you can break traditional roles into individual, composable actions and create custom roles that match your exact organizational needs. Every role starts with a Read baseline, and you add only the permissions you want — precision without complexity.

Image #1

With this release, you can:


  • Control stack operations:

    • Create, delete, and manage environment variables.

    • Lock/unlock stacks.

  • Control run actions:

    • Confirm, apply, or discard plans.

    • Trigger runs and tasks.

    • Review changes, proposed & tracked runs.

  • Attach roles to API Keys and IdP Groups.

  • Manage Contexts and Worker Pools with team-specific privileges.


Advanced Access Control mirrors your org structure, making it easy to:

  • Accelerate compliance without slowing deployments.

  • Delegate confidently to the right teams.

  • Reduce bottlenecks in permission management.

  • Streamline onboarding with reusable, self-documenting roles.


As always, we’d love your feedback, especially as we expand AAC to more resources in future releases.

New

Introducing Centralized Integrations View

We’ve introduced a new Integrations page in Spacelift to consolidate and simplify the way you manage integrations with third-party tools. This makes the interface cleaner and gives you a unified view of all the available integrations that work out of the box.You can still integrate with any tool you want by using lifecycle hooks, webhooks, API keys, the notification policy, and the ability to bring your own images.

Image #1

Right now, the available integrations you can find on this page include:

  • Backstage – Expose Spacelift stacks and runs in your developer portal.

  • ServiceNow – Connect infrastructure activity to your ITSM workflows.

  • Microsoft Teams – Push infra change and approval notifications to your Teams channels.

  • Datadog – Monitor application performance directly from Spacelift.

  • Google Cloud Platform – Authenticate with GCP using federated identity.

  • Webhooks – Deliver structured event data to external systems.

We’ll be migrating existing integration pages into this new view over time to provide a single, streamlined management experience.As always, we encourage your feedback, so let us know what you think about this new page.

New

Earlier updates